User Acceptance Testing is where a pharmaceutical company proves that a computerized system is fit for its intended use. It is also one of the most labor-intensive steps in computer system validation.
Most of that effort does not go into finding risk. It goes into writing, formatting, reviewing and reconciling documents. Regulators do not ask for that paperwork. 21 CFR Part 11, EU GMP Annex 11, GAMP 5 (2nd ed.) and FDA's 2025 Computer Software Assurance guidance all ask for the same thing: confidence, proportionate to risk, backed by trustworthy evidence.
Our white paper, Efficient UAT for GxP Systems, looks at the gap between what is required and what companies actually produce. That gap is where efficiency lives. This post is a short tour. The full paper is a free PDF.
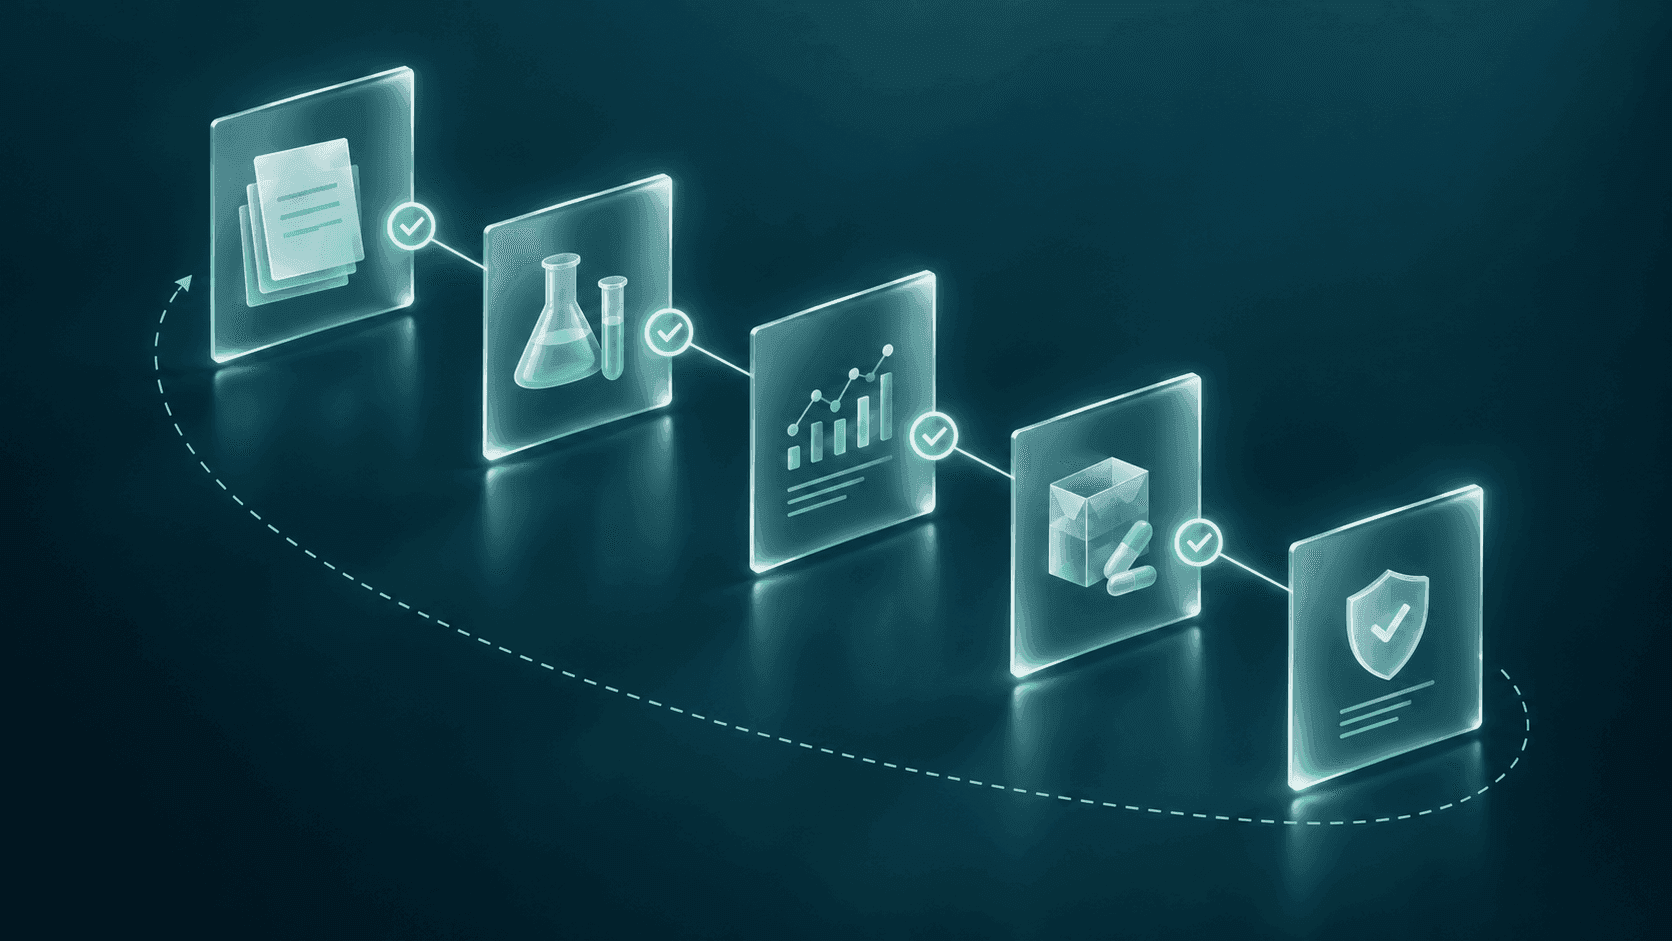
Five stages, one approval chain
Merivane supports every UAT stage: it drafts, links, checks and assembles. People review and e-sign each output before it counts as validation evidence.
UAT lifecycleProcess owner and QA e-sign at every stage
Requirements and riskFlags untestable requirements; proposes GxP risk tiers
E-signed
Test designDrafts scripted and unscripted tests scaled to each risk tier
E-signed
Execution and evidenceCaptures results and evidence as audit-trailed, e-signed GxP records
E-signed
DeviationsLinks each failure to its test, classification, fix and re-test
E-signed
Report and releaseBuilds the summary report and traceability from executed results
E-signed
Each SaaS release or changeRe-enters at requirements via impact assessment and targeted regression
Each SaaS release or change starts the cycle again at requirements, through an impact assessment.
Where UAT effort goes today
UAT in pharma is slow mainly because of how it is documented, not because of what it tests. The paper lists seven bottlenecks. Three of them show the pattern:
Manual test authoring. Validation staff hand-write step-by-step scripts from the URS, often again for every system and release. Execution waits weeks.
Uniform rigor. Every requirement gets full scripts and screenshots, whatever its GxP impact. Effort goes to low-risk features, and reviewers are fatigued when they reach the high-risk ones.
Spreadsheet traceability. Requirements, risks, tests and results are linked by hand in Excel. Gaps are found late, often by auditors.
The result is a compliance record that is large but not necessarily strong.
Put rigor where the risk is
No regulation mandates a specific UAT format, screenshot count or script style. A company that tests less on low-risk functions, leverages supplier evidence and uses system-generated records is aligned with regulatory intent.
The paper sets out three risk tiers. High-risk functions, such as batch disposition, e-signature approval and audit trail, get scripted tests with negative and boundary cases. Low-risk functions, such as cosmetic UI, get a brief record of scope and outcome. One thing does not scale down: the Part 11 and Annex 11 data integrity controls in your own configuration must be challenged in every UAT.
Risk-based test approach3 of 12 functions
Function
Impact
Level
Approach
Approve batch record
Patient safety
High
Scripted
Print certificate
Data integrity
Medium
Unscripted, with objectives
Change dashboard theme
None
Low
Ad hoc
Rationale: approve batch record appears in every batch and carries the highest patient-safety impact.
Test style follows GxP impact.
Traceability that is live, not reconciled
In a spreadsheet, a missing link shows up at the end. Merivane builds the traceability skeleton from the requirements, and links each failure to its test, classification, fix and re-test. The summary report and final traceability come directly from the executed records, so gaps are visible before execution, not at report stage.
OQ-2214 · RTM5 of 14 requirements shown
Requirement
Script
Steps
Result
Evidence
URS-014.1
TS-014-01
18
Pass
9f3c…a71e
URS-014.2
TS-014-02
14
Pass
4b0e…c2d9
URS-014.3
TS-014-04
21
Pass
d71a…08f4
URS-014.4
TS-014-05
17
Pass
e2c8…5b13
URS-014.5
TS-014-06
26
Fail · DEF-031
1c5f…3e6a
0 of 14 traced
Requirement-to-result coverage, with evidence for each step.
UAT that keeps up with SaaS releases
SaaS vendors ship multiple major releases a year. When each one needs a full UAT, UAT never finishes, and impact assessments are rushed or skipped. The paper recommends an impact assessment for each release and a targeted, repeatable regression suite that covers high-risk workflows and the core control set.
Merivane compares release notes and configuration changes to the requirement and risk baseline, and proposes the targeted regression scope. People approve the impact assessment and the scope.
Release cadenceTypical cycle
Release notes received
Impact scan
Regression run in sandbox
Defects triaged
Report signed
Go-live
One release cycle, from vendor release notes to go-live.
People keep the decisions
AI output is always a draft. Named, qualified people review and approve requirements, risk ratings, test scripts and reports before use. Merivane does not decide whether a system is fit for use. It prepares the evidence for the people who do.
What's inside the white paper
The UAT problem. Seven bottlenecks, and the weaknesses inspectors cite again and again.
What regulators actually require. Part 11, Annex 11, the draft Annex 11 revision and draft Annex 22, FDA CSA and GAMP 5, in one table.
A modern, risk-based UAT model. Risk tiers, and a core Part 11 / Annex 11 control test set for every GxP system.
Where Merivane.ai helps. Stage by stage: today's manual effort, what the platform does, and what people still do.
Using AI in validation compliantly. Five principles mapped to Part 11, Annex 11 and draft Annex 22.
Expected benefits and adoption roadmap. The metrics to baseline, and five steps from tool qualification to portfolio scale.
Conclusion.
Next step
Start with one system or one release.
The paper suggests a pilot on one medium-complexity GxP system or one SaaS release: baseline your current metrics, run UAT with Merivane, and compare authoring hours, review effort and coverage. We can help you scope it.
Vijay is a GxP technology and validation professional focused on Computer Software Assurance (CSA), risk-based testing, and the application of AI in regulated environments. He writes about modernizing validation while maintaining compliance, quality, and data integrity.